
Cloud Security: Managing Data Protection, Privacy, And Compliance Risks

Monitoring, incident response, and audit controls for cloud privacy and compliance
Monitoring and detection systems help surface anomalies, suspicious activity, and potential exfiltration attempts in cloud environments. Common telemetry sources include API access logs, object storage access records, authentication logs, and network flow data. Aggregating these sources into a centralized analysis platform enables correlation and context for alerts. Alerting strategies typically prioritize actionable events to reduce noise, and investigative playbooks outline the steps for triage, containment, and evidence preservation. Maintaining chain-of-custody details for logs and artifacts can be important for regulatory or legal processes.
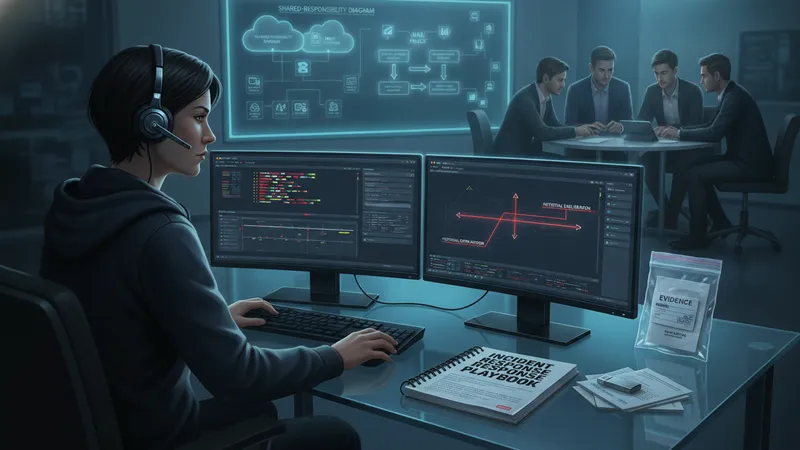
Incident response in cloud contexts often requires coordination between cloud providers and customers, reflecting the shared responsibility model. Playbooks usually document who is responsible for specific containment actions, how to collect forensic evidence without altering state, and the communication paths for internal and external stakeholders. Post-incident reviews contribute to learning and controls improvement; these reviews may update detection rules, harden IAM policies, or refine data classification practices. Regular tabletop exercises can surface gaps in coordination and telemetry availability before a real event occurs.
Audit controls and compliance evidence rely on consistent logging, policy enforcement, and documented change management. Automated evidence collection—such as configuration snapshots, policy evaluation reports, and access logs—can speed assessments and reduce manual effort. Mapping technical controls to specific regulatory requirements or contractual clauses helps clarify what evidence is required. Where external attestations are applicable, organizations often maintain copies of provider compliance reports and ensure their own policies align with those documented controls to demonstrate an end-to-end posture.
Insider considerations include validating the retention, integrity, and availability of logs; ensuring alerts include sufficient context for triage; and planning for log volume and cost. Teams may design retention tiers for different types of telemetry to balance forensic needs against storage expense. Integrating detection with workflow platforms can support timely investigations, and periodic reviews of alert effectiveness help refine thresholds. These operational details support sustained compliance and improve responsiveness to privacy-related incidents.